Key Function
Cross-Platform Computer Forensics Analysis
Supports full acquisition and analysis across Windows, macOS and Linux. It adapts to complex disk structures, encrypted partitions and damaged media, with built-in data recovery and global search capabilities for comprehensive evidence mining.
● Supports parsing for Linux MDADM software RAID and BTRFS disk arrays.
● Support structured parsing and offline forensic parsing for major encrypted partitions including BitLocker, FileVault2, VeraCrypt and LUKS, with automatic system and WiFi key recognition.
Multi-Scenario System Emulation
Features one-click automated multi-platform forensic emulation and integrated boot repair tools. Comprehensive process logging and environment recording ensure fully traceable, repeatable and judicially compliant forensic workflows.
High-Performance Disk Duplication & Imaging
Resumable processing, multi-algorithm hash verification, standardized forensic image creation and restoration, as well as compliant media sanitization are fully supported. These capabilities ensure complete evidence integrity and overall data security.
Integrated Forensic Operation & Intelligent Analysis
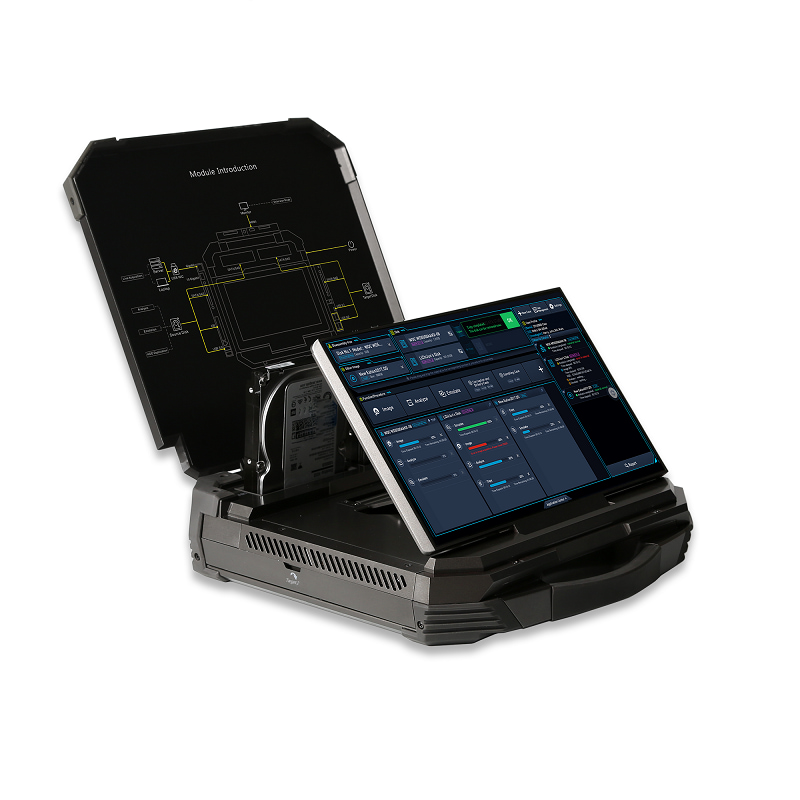
Integrate acquisition, analysis, evidence evaluation and dynamic emulation for all-in-one operation. Enable rapid evidence triage, targeted data extraction and on-demand report generation.
Core Advantage
● Maintain compatibility with mainstream commercial storage media. Enable rapid evidence preservation and high-speed data acquisition across diverse multi-interface media devices.
● Flexible Customised Deployment – Adaptable hardware and functional configurations meet differentiated forensic requirements of various law enforcement and investigation scenarios.